(SeaPRwire) – By: Helena Brooks
The digital signature on a website matters more than most people realize. For years, trusted certificate authorities quietly enforced US sanctions without reading any legislation. When a browser refused to connect to a sanctioned entity, that was sanctions enforcement. No drones, no seizures, no diplomats. Just a small padlock icon disappearing from the address bar. That infrastructure worked because the global PKI system runs through Washington-adjacent roots. Until it didn’t.
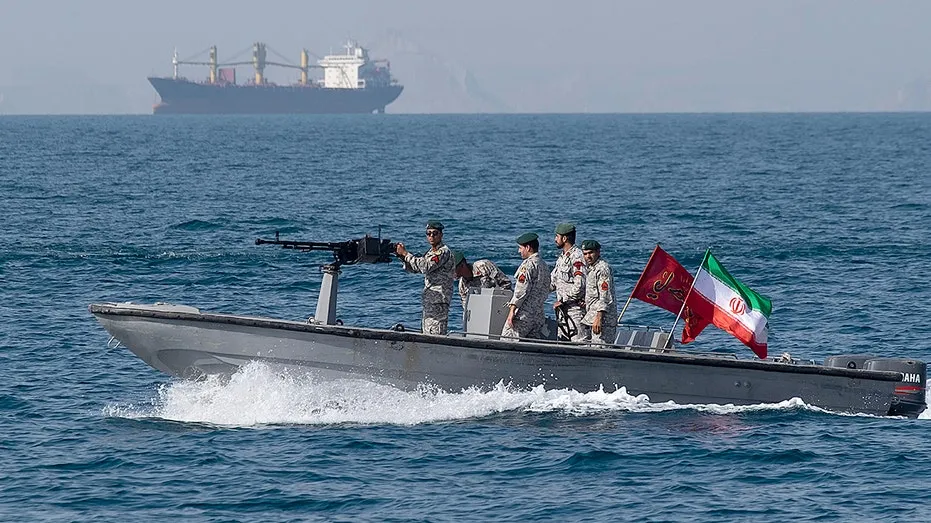
On May 27, the Treasury Department formally designated Iran’s Persian Gulf Straits Authority under Executive Order 13224, labeling it an instrument of IRGC extortion targeting vessels transiting the Strait of Hormuz. The designation triggered an immediate technical consequence. Standard SSL/TLS certificates expired or could not be renewed through Western-aligned authorities. By August 10, NetBlocks CEO Alp Toker confirmed the PGSA website had become inaccessible through normal browsers. Shipping companies attempting to interact with the portal were forced onto unencrypted HTTP connections. Toker described what happened next in stark terms. He called it a class of vulnerability open to government exploitation rather than a corporate breach. The traffic shifted into unencrypted formats. Any form submission on the site could have been eavesdropped. The Treasury warned explicitly that anyone cooperating with the so-called strait authority may be providing support to the IRGC and could face sanctions exposure themselves.
Here is where the official narrative collides with the operational reality. TrustAsia issued a Domain Validated TLS certificate for pgsa.ir through an automated validation process. The company’s own statement, delivered on August 20, confirmed the certificate was generated. The firm described DV certificates as relying entirely on automated verification of control over requested domain names. No legal identity check. No sanctions screening. No affiliation verification. The relationship described in the Digital inquiry was not identified during issuance, TrustAsia wrote. They added the entire pgsa.ir domain namespace to a restricted-issuance list following the incident and revoked the existing certificate on August 21 at 12:15:25 UTC. Toker confirmed the revocation. Most browsers will stop trusting the site once that signal propagates. TrustAsia characterized all of this as precautionary compliance and risk-control measures. They were careful to add that nothing should be interpreted as a finding that the certificate was technically misissued. The automated system worked precisely as designed. It just happened to serve a sanctioned Iranian maritime authority collecting tolls from commercial shipping traffic.
Jeremy Paner, a partner at Hughes Hubbard & Reed and former OFAC official, did not accept the automation defense. He told Digital that restoring the certificate was unequivocally sanctionable under Executive Order 13224. The authority does not require the service to be knowingly provided to the PGSA, Paner stated. The automated nature of the service is irrelevant and does not make it any less sanctionable. Anyone providing any level of services to a sanctioned Iranian company can trigger enforcement. The Treasury’s warning from May had been explicit. Service provision itself is material support. Toker offered the structural explanation for how this slipped through. Almost all root certificate authorities do business with the United States, he noted. They tend to comply with US sanctions. TrustAsia had gone its own way, building a China-first certificate infrastructure that sidesteps the West. That infrastructure choice is the actual story. Major US web browsers still recognize TrustAsia root certificates. American systems automatically trusted the sanctioned Iranian portal for four days.
The emerging pattern is clear enough to trace. Western CAs enforce sanctions indirectly through browser trust stores and automated compliance chains. Chinese CAs are constructing parallel PKI pathways that bypass those same trust anchors. The moment those alternate roots gain traction in non-Western browsers and operating systems, the enforcement gap becomes structural rather than incidental. Toker’s point about Iran finding another certificate authority if TrustAsia’s revocation sticks confirms the substitution risk. Sanctions enforcement through digital infrastructure depends on concentrated trust. Decentralized trust distributes that enforcement power. China is building the distribution network.
Expect OFAC to target not just the specific service provision but the broader compliance architecture going forward. The legal threshold for sanctioning foreign providers of services to designated Iranian entities is already broad under current executive orders. Automation defenses have no standing before that authority. Companies issuing certificates to domains tied to sanctioned entities should assume discovery will follow and compliance programs will be examined retroactively. The TrustAsia incident is not a compliance glitch. It is an architectural fault line. The next wave of enforcement will aim at the infrastructure itself rather than individual transactions.
Author bio: Helena Brooks is a financial intelligence tracking expert and advisor on illicit capital flows, specializing in sanctions arbitrage and dual-use supply network analysis.